O365HIGH SEVERITY
Incident Analysis
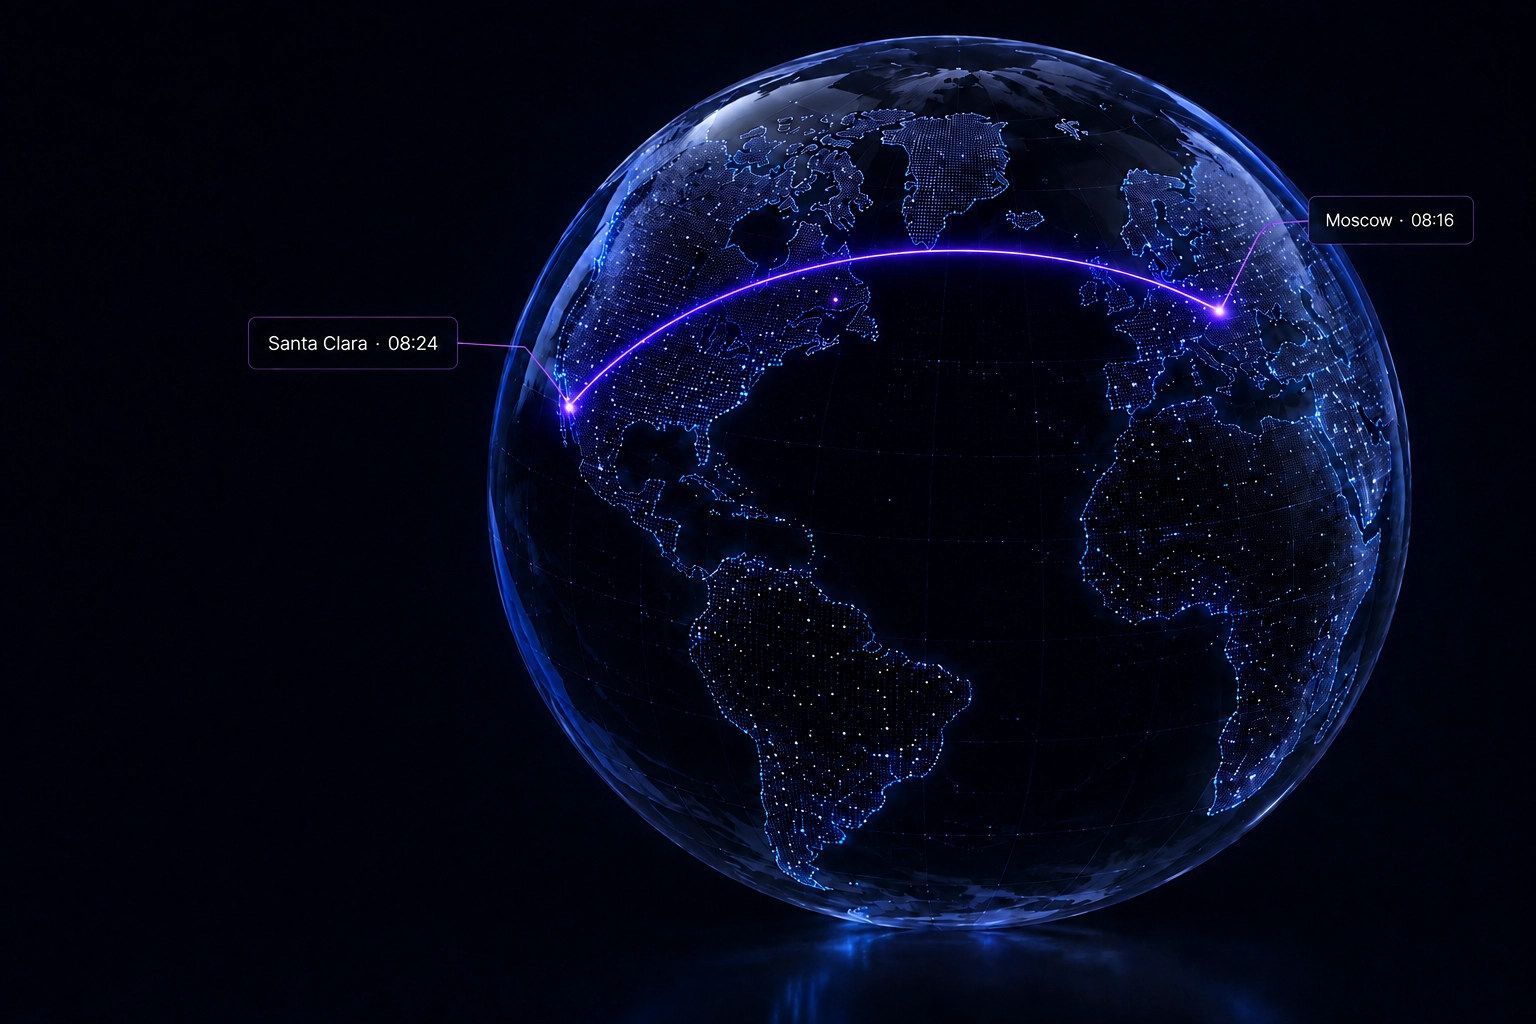
Impossible Travel
Investigating Sign-ins
Moscownew sign-in
Santa Claradevice changed
Identity AnalystSOC Commander
InvestigateCorrelateContain
NextSOC adds autonomous investigation and response across your existing security stack, using specialized AI agents to investigate alerts, correlate evidence, and mitigate threats.
A sign-in that needs a closer look.
Moscownew sign-in
Santa Claradevice changed
01 THE CHALLENGE
Your team’s attention is finite.
The demands on your SOC aren’t.
The cybersecurity workforce shortage leaves organizations unable to staff 24/7 coverage, creating dangerous blind spots.
Always-on investigationsAnalysts are buried under floods of noisy alerts, increasing the chance of missing critical threats.
Security leaders must strengthen defenses with limited resources. Traditional hiring and tools do not scale.
Attackers innovate daily with ransomware, supply chain compromises, and AI-powered tactics.
Regulatory complexity creates business risk. Non-compliance means fines, reputational damage, and lost trust.
02 WHAT IS NEXTSOC?
NextSOC is an agentic security operations platform for autonomous investigation and response across your existing security stack.
01 / AI Engine
Bring alerts from across your stack into one consistent, enriched view before an investigation begins.
03 WHY NEXTSOC
NextSOC adds agentic investigation and response to existing security teams, IT teams, and managed services—without forcing you to replace the tools and workflows you already use.
| Why it matters | Traditional approach | NextSOC |
|---|---|---|
| Existing stack | Adding more tools often creates more workflows, integrations, and operational overhead. | Works across the security and IT stack already in place. |
| Investigation | Analysts gather and correlate evidence manually across multiple tools. | Specialized AI agents investigate, enrich, and correlate evidence autonomously. |
| Response | Recommendations still require analysts to determine and execute the next steps. | Produces decision-ready actions and can execute approved response actions across supported systems. |
| Coverage | Triage often focuses on the highest-severity alerts. | Investigates broadly across identity, cloud, network, endpoint, email, and data, including lower-severity signals with hidden risk. |
| Scale | More alerts, users, or customers typically require more analyst capacity. | Agentic operations expand investigation and response capacity without requiring headcount to scale at the same rate. |
| MSP / MSSP | Managed services often scale through additional analysts, process, and operational overhead. | Adds autonomous investigation, decision support, and response capabilities to an existing managed service. |
| Lean teams | Building a traditional SOC requires significant staffing, tooling, and operational coverage. | Adds SOC capabilities to an existing security or IT team without requiring a full traditional SOC. |
| Human control | Operations are often either highly manual or dependent on rigid automation. | Automates where appropriate while keeping people in control of sensitive actions through evidence, policy boundaries, and approval gates. |
EARLY ACCESS
Add autonomous investigation and response to the tools and team you already have.
Request early access